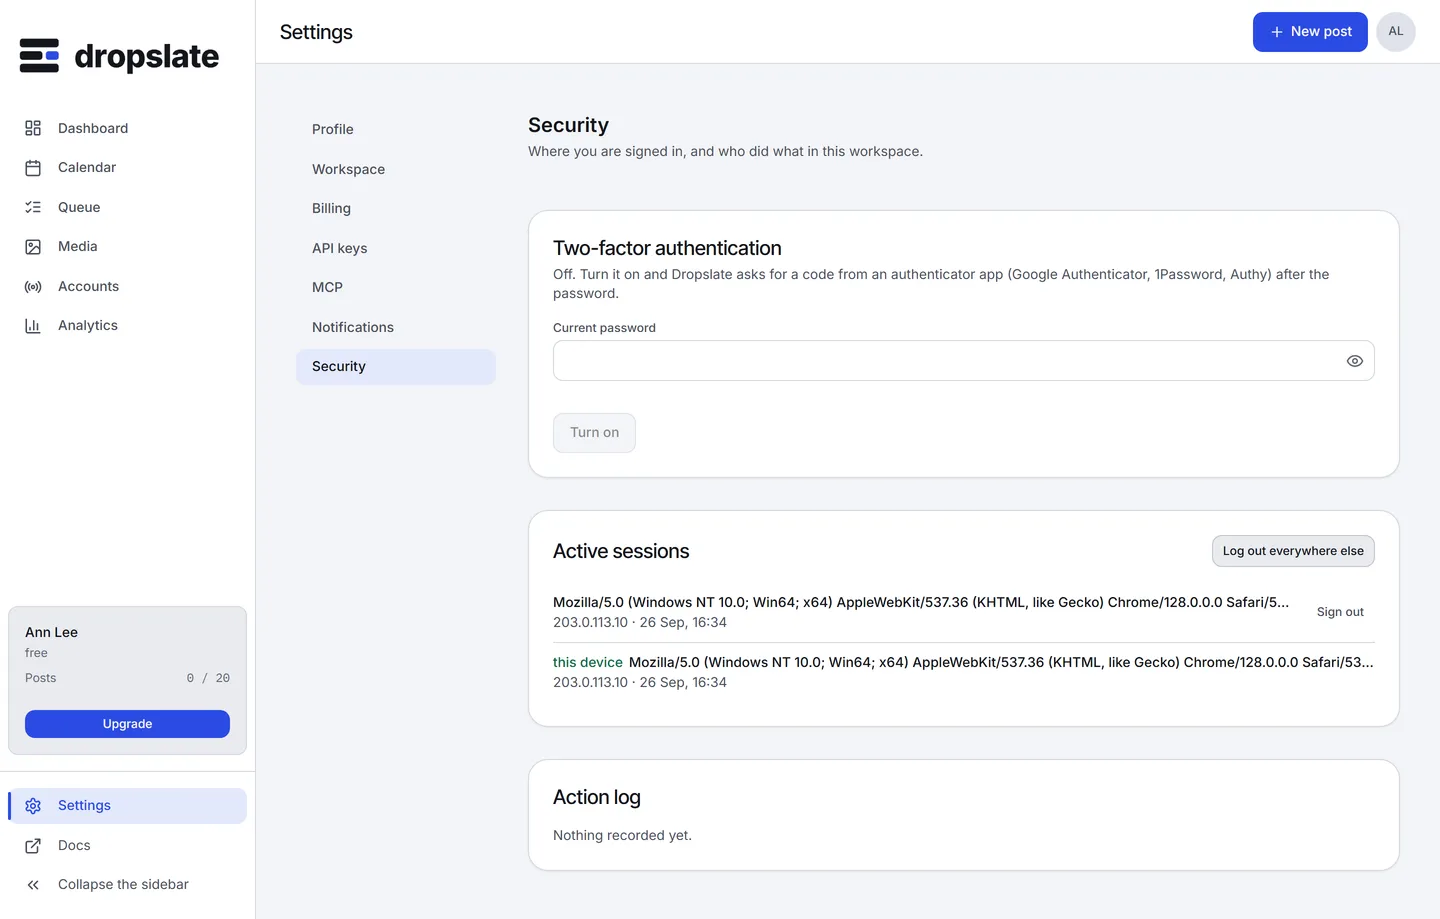
Security
What this is
Section titled “What this is”The full security statement is at dropslate.top/security; this page is the short, task-oriented version for anyone building against the API or MCP.
What matters for an integration
Section titled “What matters for an integration”- Tokens never leave the server. A connected account’s OAuth token is encrypted at rest (AES-256-GCM) and decrypted only inside the one call that needs it. No API, MCP or dashboard response ever contains it.
- Every query is workspace-scoped. An id from another workspace answers
not_found, identical to one that doesn’t exist - never aforbiddenthat would confirm it exists. See Errors. - Media is served through signed URLs. A file’s URL is time-limited and tied to that specific file; the storage path itself is never listable or guessable.
- MCP and API keys are scoped and audited.
read/write, nothing more; every call is written to the workspace’s own audit log; nothing that touches members, billing or connected accounts is reachable this way at all - see MCP → Safety rules. - Card data never reaches Dropslate’s servers. Checkout and invoices run on the payment provider’s hosted pages - see Invoices.
Report a problem
Section titled “Report a problem”Email security@dropslate.top - receipt is confirmed within 48 hours.
Common errors
Section titled “Common errors”| Error | Cause | Fix |
|---|---|---|
not_found on a resource you’re sure exists |
It belongs to a different workspace than the credential you’re using. | Confirm which workspace the key or session belongs to with dropslate_whoami or GET /whoami. |